nette-markdown
nette-markdown is a Nette extension that converts Markdown to HTML with league/commonmark and adds a Latte |markdown filter that strips input HTML and blocks javascript: links.
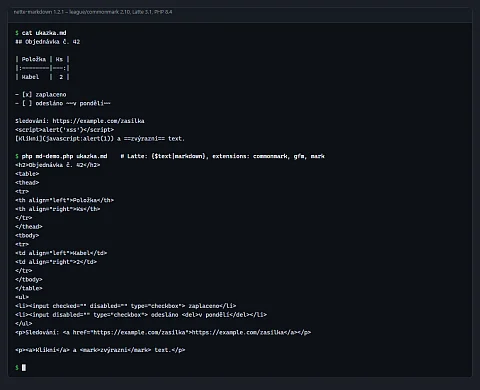
nette-markdown is a Nette extension that converts Markdown to HTML through the league/commonmark library and adds a |markdown filter to Latte templates. It fits anywhere text is written by people outside the editorial team: comments, product descriptions from sellers, helpdesk replies, an internal wiki. Users want a table, bullet points and a link, but as soon as a form allows HTML, sooner or later someone pastes in a <script> or a link with javascript:. Markdown gives the formatting people know from GitHub and chat apps, and nette-markdown makes sure nothing executable reaches the page from it.
What the filter does with untrusted text
The screenshot above shows a real conversion. The input contained a heading, a table with column alignment, a task list, struck-through text, a bare URL, a <script> tag, the link [Klikni](javascript:alert(1)) and the highlight ==zvýrazni==. The output has a table with align="left" and align="right", checkboxes as disabled <input> elements, strikethrough as <del>, the URL turned into a link and the highlight as <mark>. The <script> tag disappeared entirely, content included, and all that was left of the link was its text in an <a> without an href attribute. The template contained a single line, {$text|markdown}; the converter was configured with the commonmark, gfm and mark extensions.
Two filters for two levels of trust
The extension registers three filters on every Latte\Engine in the container. |markdown and |markdownSafe always use the safe conversion: HTML in the input is removed and links with schemes such as javascript:, vbscript: or data: are blocked, whatever the configuration says. The safe conversion uses the extensions from the configuration (footnotes, table of contents, highlighting), which is why ==zvýrazni== became <mark> in the screenshot; it enforces only html_input: strip and allow_unsafe_links: false. |markdownRaw converts exactly according to the configuration, including html_input: allow, and belongs only on text from your own editors. The filters return a Latte\Runtime\Html object, so Latte does not escape the output a second time and |noescape is not written.
In a presenter or service, MarkdownConverter is available with the same two methods, convert() and convertSafe(). It can also be created without Nette, with a plain new MarkdownConverter().
Extensions for what the text needs
The default set is CommonMark plus GFM: tables, task lists, strikethrough and autolinks. Six more are switched on by name in the configuration:
footnotefor footnotes in the form[^1],smartpunctfor typographic quotes, dashes and ellipses,heading_permalinkfor heading anchors with a configurable symbol,tocfor a table of contents built from headings,markfor==text==rendered as<mark>, the package's own extension,external_linkfor outbound links withrel="nofollow noopener noreferrer", an exception for your own domains and optional opening in a new window.
A typo in an extension name does not pass silently: the constructor throws an InvalidArgumentException listing the known names. The HTML input mode has three values, strip (the default), escape and allow, and the configuration schema accepts no other.
Why not wire up commonmark yourself
league/commonmark on its own can do everything listed above, but in a Nette application someone has to build the environment, register the extensions, add the filter to Latte and make sure every template showing untrusted text uses the safe variant. This package does it with one line in config.neon and puts the safe variant under the shortest name, so the shorter thing to type is also the safer one.
Tests and releases
The repository has 22 PHPUnit 10 tests with 43 assertions: tables, task lists, strikethrough, autolinks, code blocks, HTML stripping, blocking unsafe links, footnotes, heading anchors, an unknown extension, outbound link attributes, mark highlighting, safe conversion with the configured extensions and the Latte filters. They all passed on PHP 8.2 and 8.4. GitHub Actions runs them on PHP 8.2, 8.3 and 8.4 and, after a successful run, updates the package on Packagist.
Getting started
composer require nks-hub/nette-markdownextensions:
markdown: NksHub\Markdown\DI\MarkdownExtension
markdown:
extensions: [commonmark, gfm, footnote, mark]
html_input: stripIt needs PHP 8.2 or newer, league/commonmark 2.8+, nette/di 3.1 and Latte 3. Version 1.2.0 from 22 March 2026 switched the default filter to the safe conversion and added the outbound link attributes; the latest is 1.2.1 from 6 November 2026.
Source code
The code is on GitHub in the nks-hub/nette-markdown repository under the MIT licence, and the package is on Packagist as nks-hub/nette-markdown. An editor with a toolbar for Markdown and Texy is a separate project, texy-ts-editor.